Microsoft Copilot Review: What Phoenix Small Businesses Should Know Before Adopting It
This reviews what Microsoft Copilot function, cost, and what Phoenix business owners should consider before signing an annual Copilot contract.
4 min read
Jordan Hetrick
:
Published
Updated
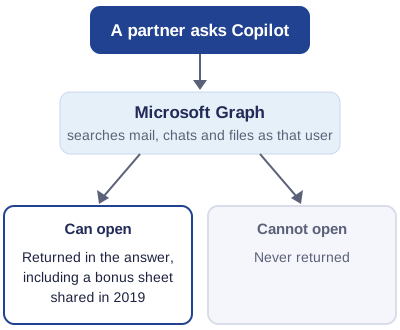
Picture a managing partner at a CPA firm asking Copilot to pull together everything the firm has on a client's engagement. It works. It also returns a spreadsheet of staff bonuses that has sat in a shared folder since 2019. Nobody broke in. Copilot did its job, and the firm's permissions did the rest.
The short answer
A Copilot readiness audit is the permissions work a CPA firm finishes before it assigns the first Microsoft 365 Copilot license. Microsoft says Copilot draws on the mail, chats and files of the signed-in user through Microsoft Graph, so it reaches only what that person can open. So every overshared SharePoint site, stale guest account and forgotten folder becomes searchable by a plain-English question. The audit runs in four steps. Review permissions on every SharePoint site and shared drive. Run a site access review so owners trim what nobody needs. Pilot with a small group, and widen the rollout only once access stabilizes. Then apply sensitivity labels that encrypt where Copilot should not summarize a file. Skip these steps and the first thing Copilot shows a partner is your permissions debt. Do the governance work first, and the licensing decision is the easy part.
Copilot can surface anything the signed-in user can already reach. This sounds harmless until you remember how permissions accumulate. Every file someone was mistakenly granted, every SharePoint site shared with the whole organization years ago, every folder inherited from a departed employee becomes reachable through a chat prompt, with no deliberate search needed. Assign licenses before a tenant readiness review, and Copilot shows staff whatever the firm has already overshared. That makes a rollout a governance project first and a licensing project second. The pre-rollout work includes a permissions audit across sites and shared drives, sensitivity labels applied through Microsoft Purview, and an access review to remove what nobody should still be able to access. A firm that skips it will discover its permissions debt from a partner’s chat window.
Copilot reaches only what the signed-in user can open, as Microsoft documents it.
Microsoft's training material sets the bar at View permission across SharePoint, OneDrive, and Teams. That is the security model working as intended. The weak point is the permission layer underneath it, which most firms never audit. Microsoft's own SharePoint guidance for Copilot tells administrators to find overshared content with its governance reports, to prevent accidental oversharing in Copilot. A misfiled document used to stay hidden because nobody knew where to look. Now, a plain-English question does the looking.
The September 2026 column in CPA Practice Advisor calls Copilot the safest AI product for documents that contain client data. That safety describes where the data travels. It does not change which staff inside the firm can reach client tax records and engagement files.
A license switches on that access path for a specific person. Treating it as a purchasing task hides the real decision: who gets a search engine over everything they can touch.
The admin center's readiness report covers license eligibility and update channels. Microsoft's tenant readiness training lists a SharePoint governance and data-readiness review as its own checklist item, one that checks for oversharing and stale permissions before Copilot can surface content through them. A green licensing report and a clean permission model are different things.
Policy is the second gap. An AI policy written last year usually answers one narrow question: whether staff can paste client data into a public chatbot. Copilot raises a different set. Who owns each SharePoint site? Which guests still have access? How long do chats and files live? Does the engagement letter cover AI-assisted work? Who decides what agents can reach? PK Tech walks firms through important questions to consider, and a policy written last year rarely answers them. The tool changed what staff can do without asking anyone, so the policy has to change with it.
Start with permissions. The data access governance reports in SharePoint Advanced Management give you a baseline of existing oversharing, and activity reports catch new oversharing as it happens.
Next, run an access review. A site access review allows an administrator to hand off a flagged site to its owner, who verifies and manages who has access. Owners know whether the tax-planning site really needs 60 members.
Some sites cannot be fixed before launch. Microsoft gives you three controls for those, and only two are worth using.
| What it doesPer Microsoft's training | Use itFor a CPA firm | |
|---|---|---|
| Restricted Content Discovery | Hides a site from organization-wide search and Copilot's broad discovery. Permissions stay as they are | Sites you cannot fix before launch. It buys time |
| Restricted Access Control | Limits a site to named groups | When hiding a site is not enough |
| Restricted SharePoint Search | Legacy behavior. New enablement blocked since July 31, 2026 | Skip it |
Rollout order
Six steps before the license goes out
PK Tech packages this as a tenant readiness engagement. We baseline the tenant, fix permissions, and configure Microsoft 365 Business Premium with Defender and Purview so that the controls are in place before the licenses are. Business Premium already includes Defender for Business, and Microsoft's Purview Suite add-on for Business Premium adds default labels for SharePoint libraries, automatic labeling, and DLP for Microsoft 365 Copilot.
A label is not a lock
Not by themselves. A “Confidential” label does not stop Copilot from finding a file.
Protection arrives when the label applies encryption. The table shows what each option does.
| Marking label“Confidential” only | Encrypting labelWith usage rights | Encryption, no EXTRACTFor files at rest | DLP for CopilotBy label | |
|---|---|---|---|---|
| What it does | Tells people how to handle the file | Encrypts the file | Encrypts it and withholds EXTRACT | Keeps Copilot away from content with chosen labels |
| Copilot | Still retrieves it for anyone who can open it | Returns it to anyone holding VIEW and EXTRACT, which most staff have unless the firm restricts them | Does not summarize it | Stays out of the labelled content |
| Source | Microsoft | Microsoft Purview | Purview guidance | DLP for Copilot |
Copilot will earn its place at your firm. What you control is whether the first thing it shows a partner is a useful answer or a forgotten permission.

For CPA firms
Get your tenant ready for Copilot with PK Tech
PK Tech has worked with CPA firms as a managed IT provider for more than 16 years, and holds AICPA SOC 2 Type II attestation from an independent audit. If a Copilot rollout is on your calendar, bring your SharePoint site list and we will review your security defaults and permissions before you begin.
Schedule a call with Jordan →
This reviews what Microsoft Copilot function, cost, and what Phoenix business owners should consider before signing an annual Copilot contract.
This blog will provide a clear picture of what Microsoft’s AI ecosystem actually looks like for business owners in Phoenix.
This post breaks down what the data shows on Copilot adoption, where the real gains tend to appear, and how to build a measurement approach.